JWT Security: Vulnerabilities, Attacks and Best Practices
How pentesters break JSON Web Tokens - algorithm confusion, weak HMAC secrets, kid and jku injection, claim validation flaws - and the defenses that stop them.
How pentesters break JSON Web Tokens - algorithm confusion, weak HMAC secrets, kid and jku injection, claim validation flaws - and the defenses that stop them.
Learn how a new type of cyberattack, RA-ICA, quietly drains API tokens and inflates the running costs of corporate AI and RAG systems by up to 1,300%.
A practical guide for parents and schools on protecting children online from cyberbullying, phishing, grooming, deepfake misuse and harmful content.
AI is not only a threat. It helps detect phishing, analyze incidents, filter threats and speed up the response of security teams.
AI phishing is more convincing than ordinary scam messages. Learn how to recognize email phishing, smishing, vishing and spear phishing.
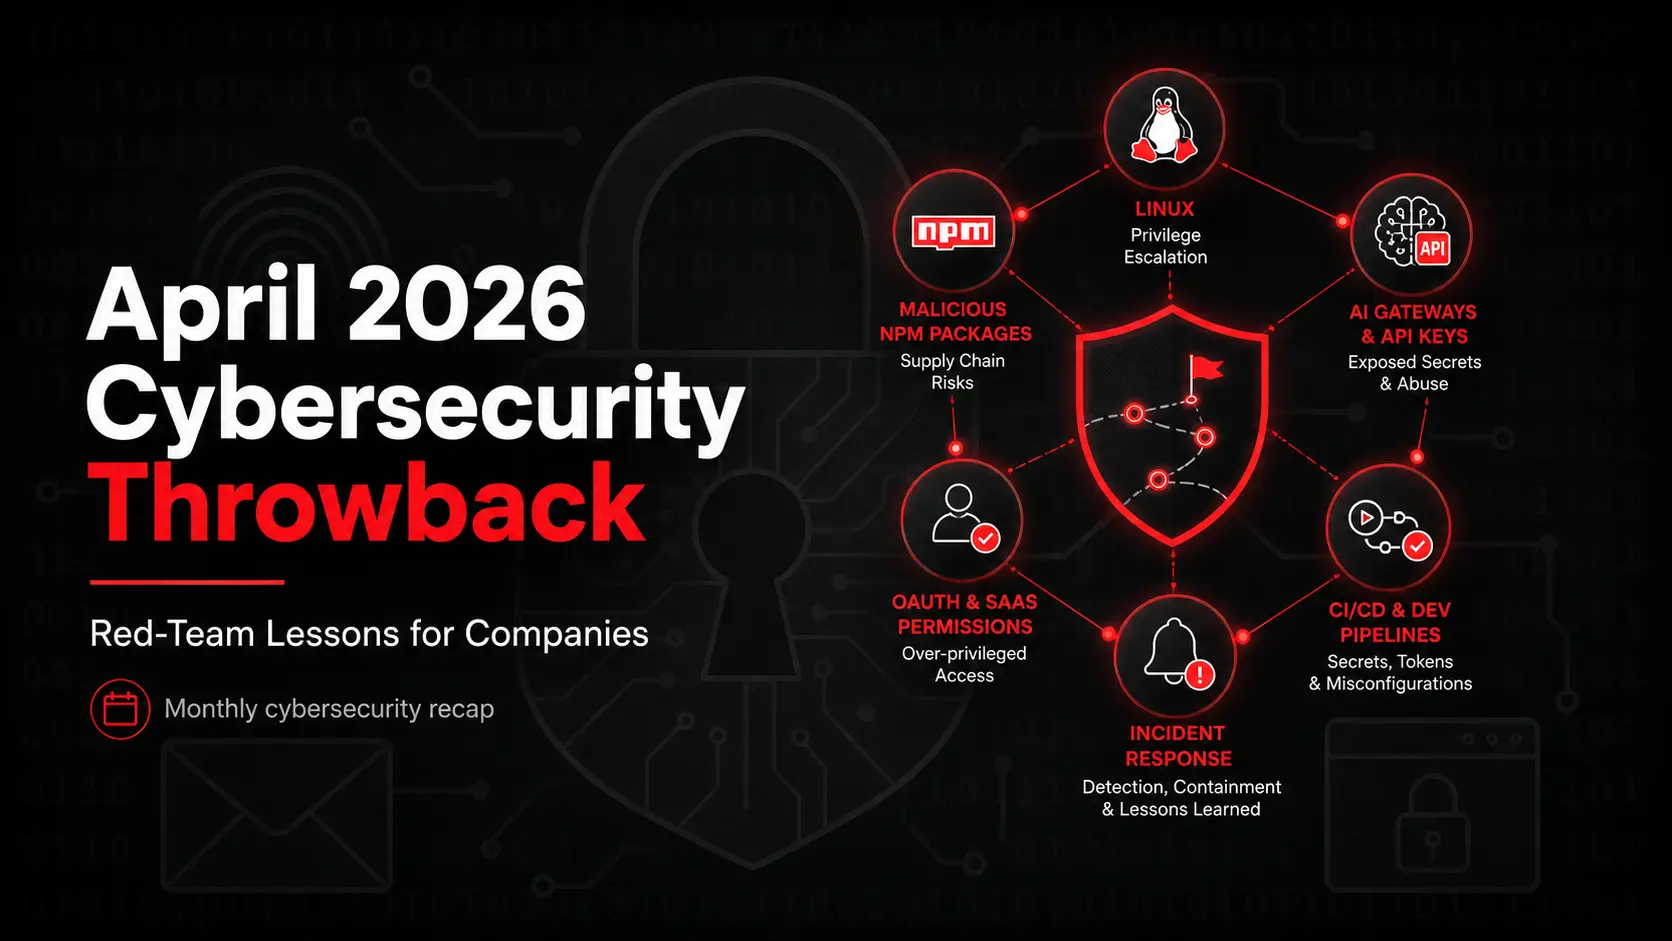
Red-team analysis of April 2026: Copy Fail, npm supply chain, AI security, OAuth, CI/CD, cloud, vulnerability management and incident response.
Deepfake voice and vishing can imitate a CEO, colleague or family member. Learn the warning signs and how to verify suspicious calls.
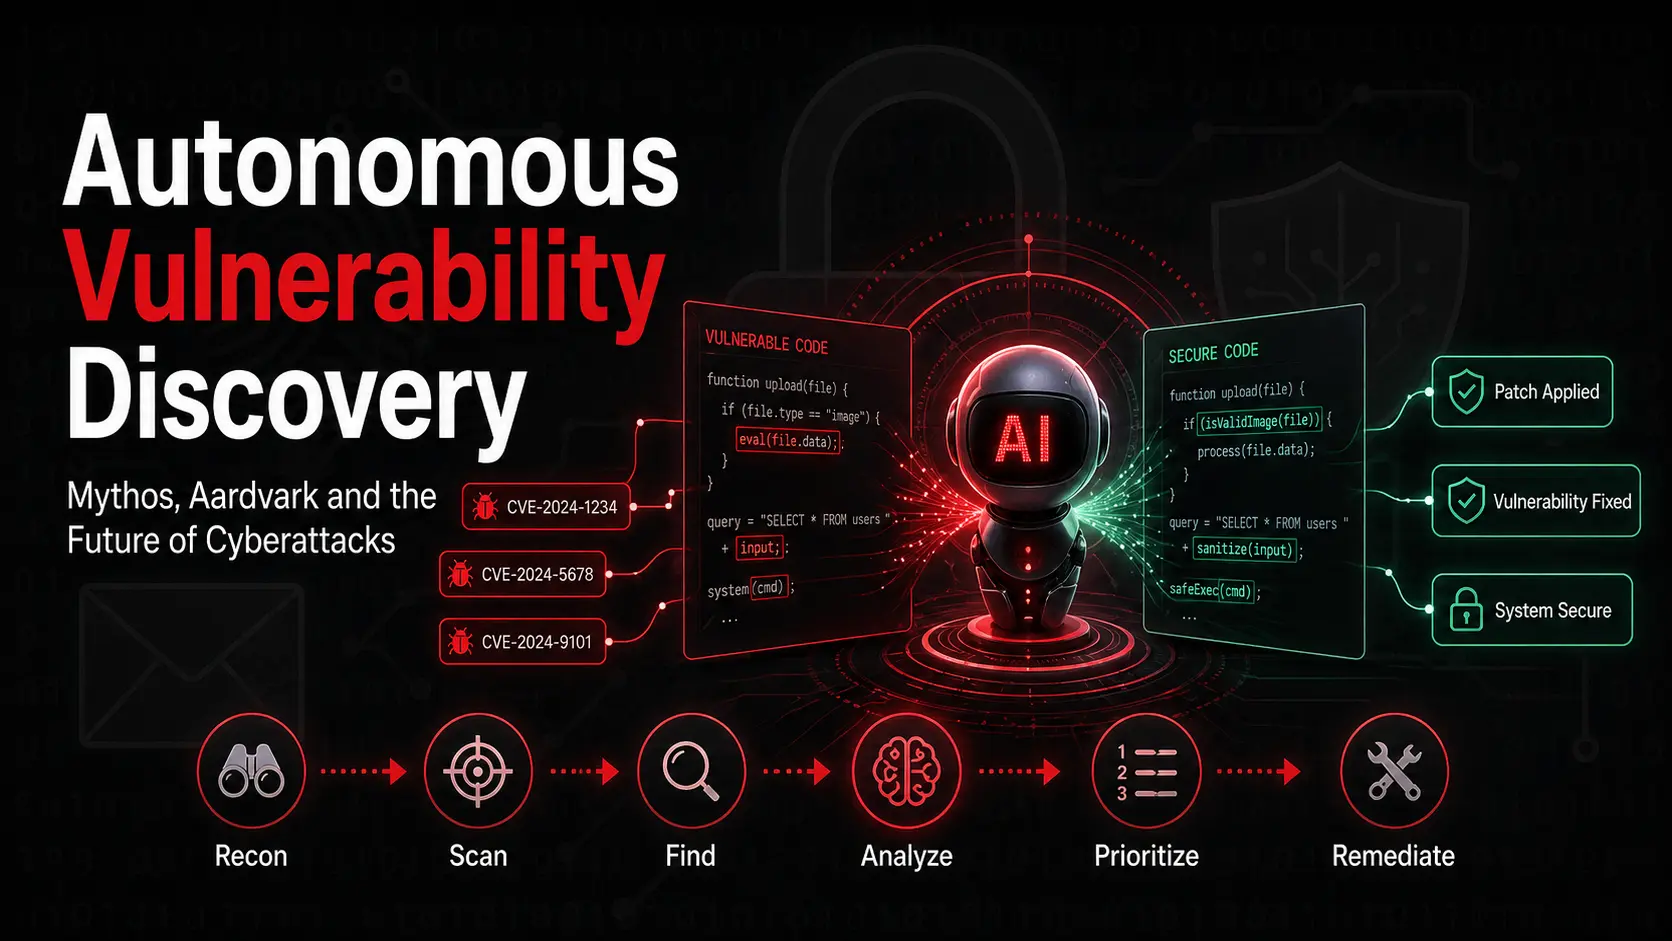
AI models such as Mythos and Aardvark show that vulnerability discovery can become faster and more automated. What does this mean for businesses?
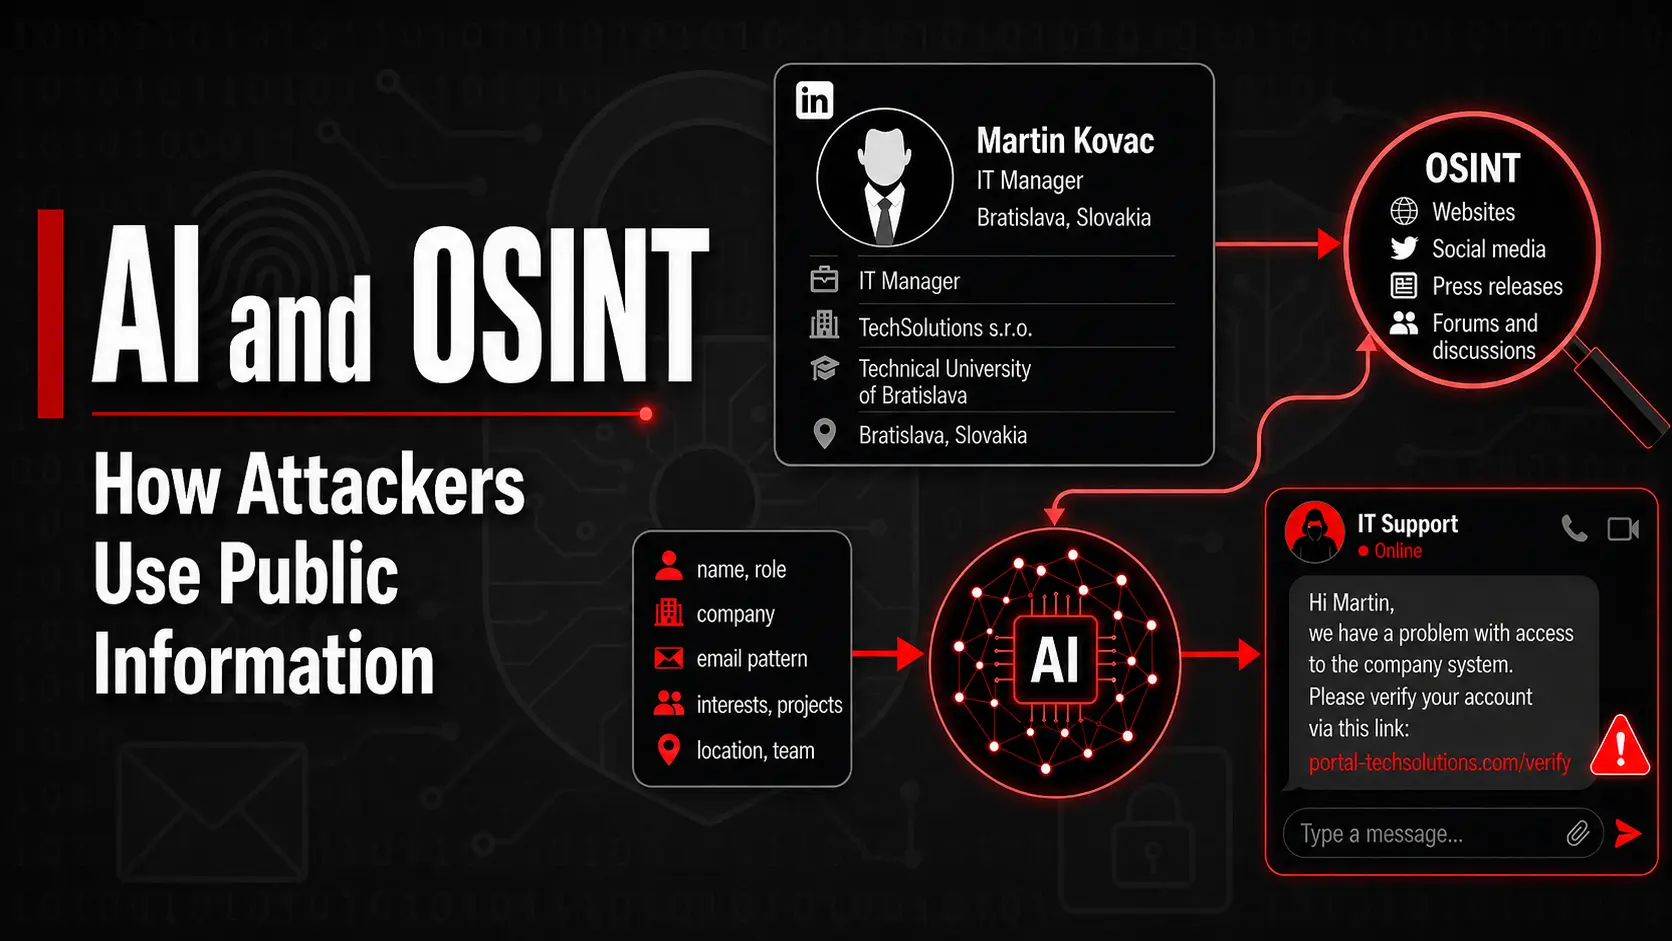
Attackers use LinkedIn, social media and company websites to build personalized scams. Learn how OSINT, AI and pretexting work in real attacks.
Artificial intelligence is changing phishing, deepfake scams and vulnerability discovery. Learn how attackers use AI and how to protect your business.
CVE-2026-24061 is a critical GNU InetUtils telnetd authentication bypass that can grant unauthenticated root access. Learn what happened, why even well-maintained networks are at risk, and why assumed breach penetration testing matters.
How an ethical hacker works, how banks and clouds are tested, why North Korea steals crypto - and how you can be hacked without noticing.
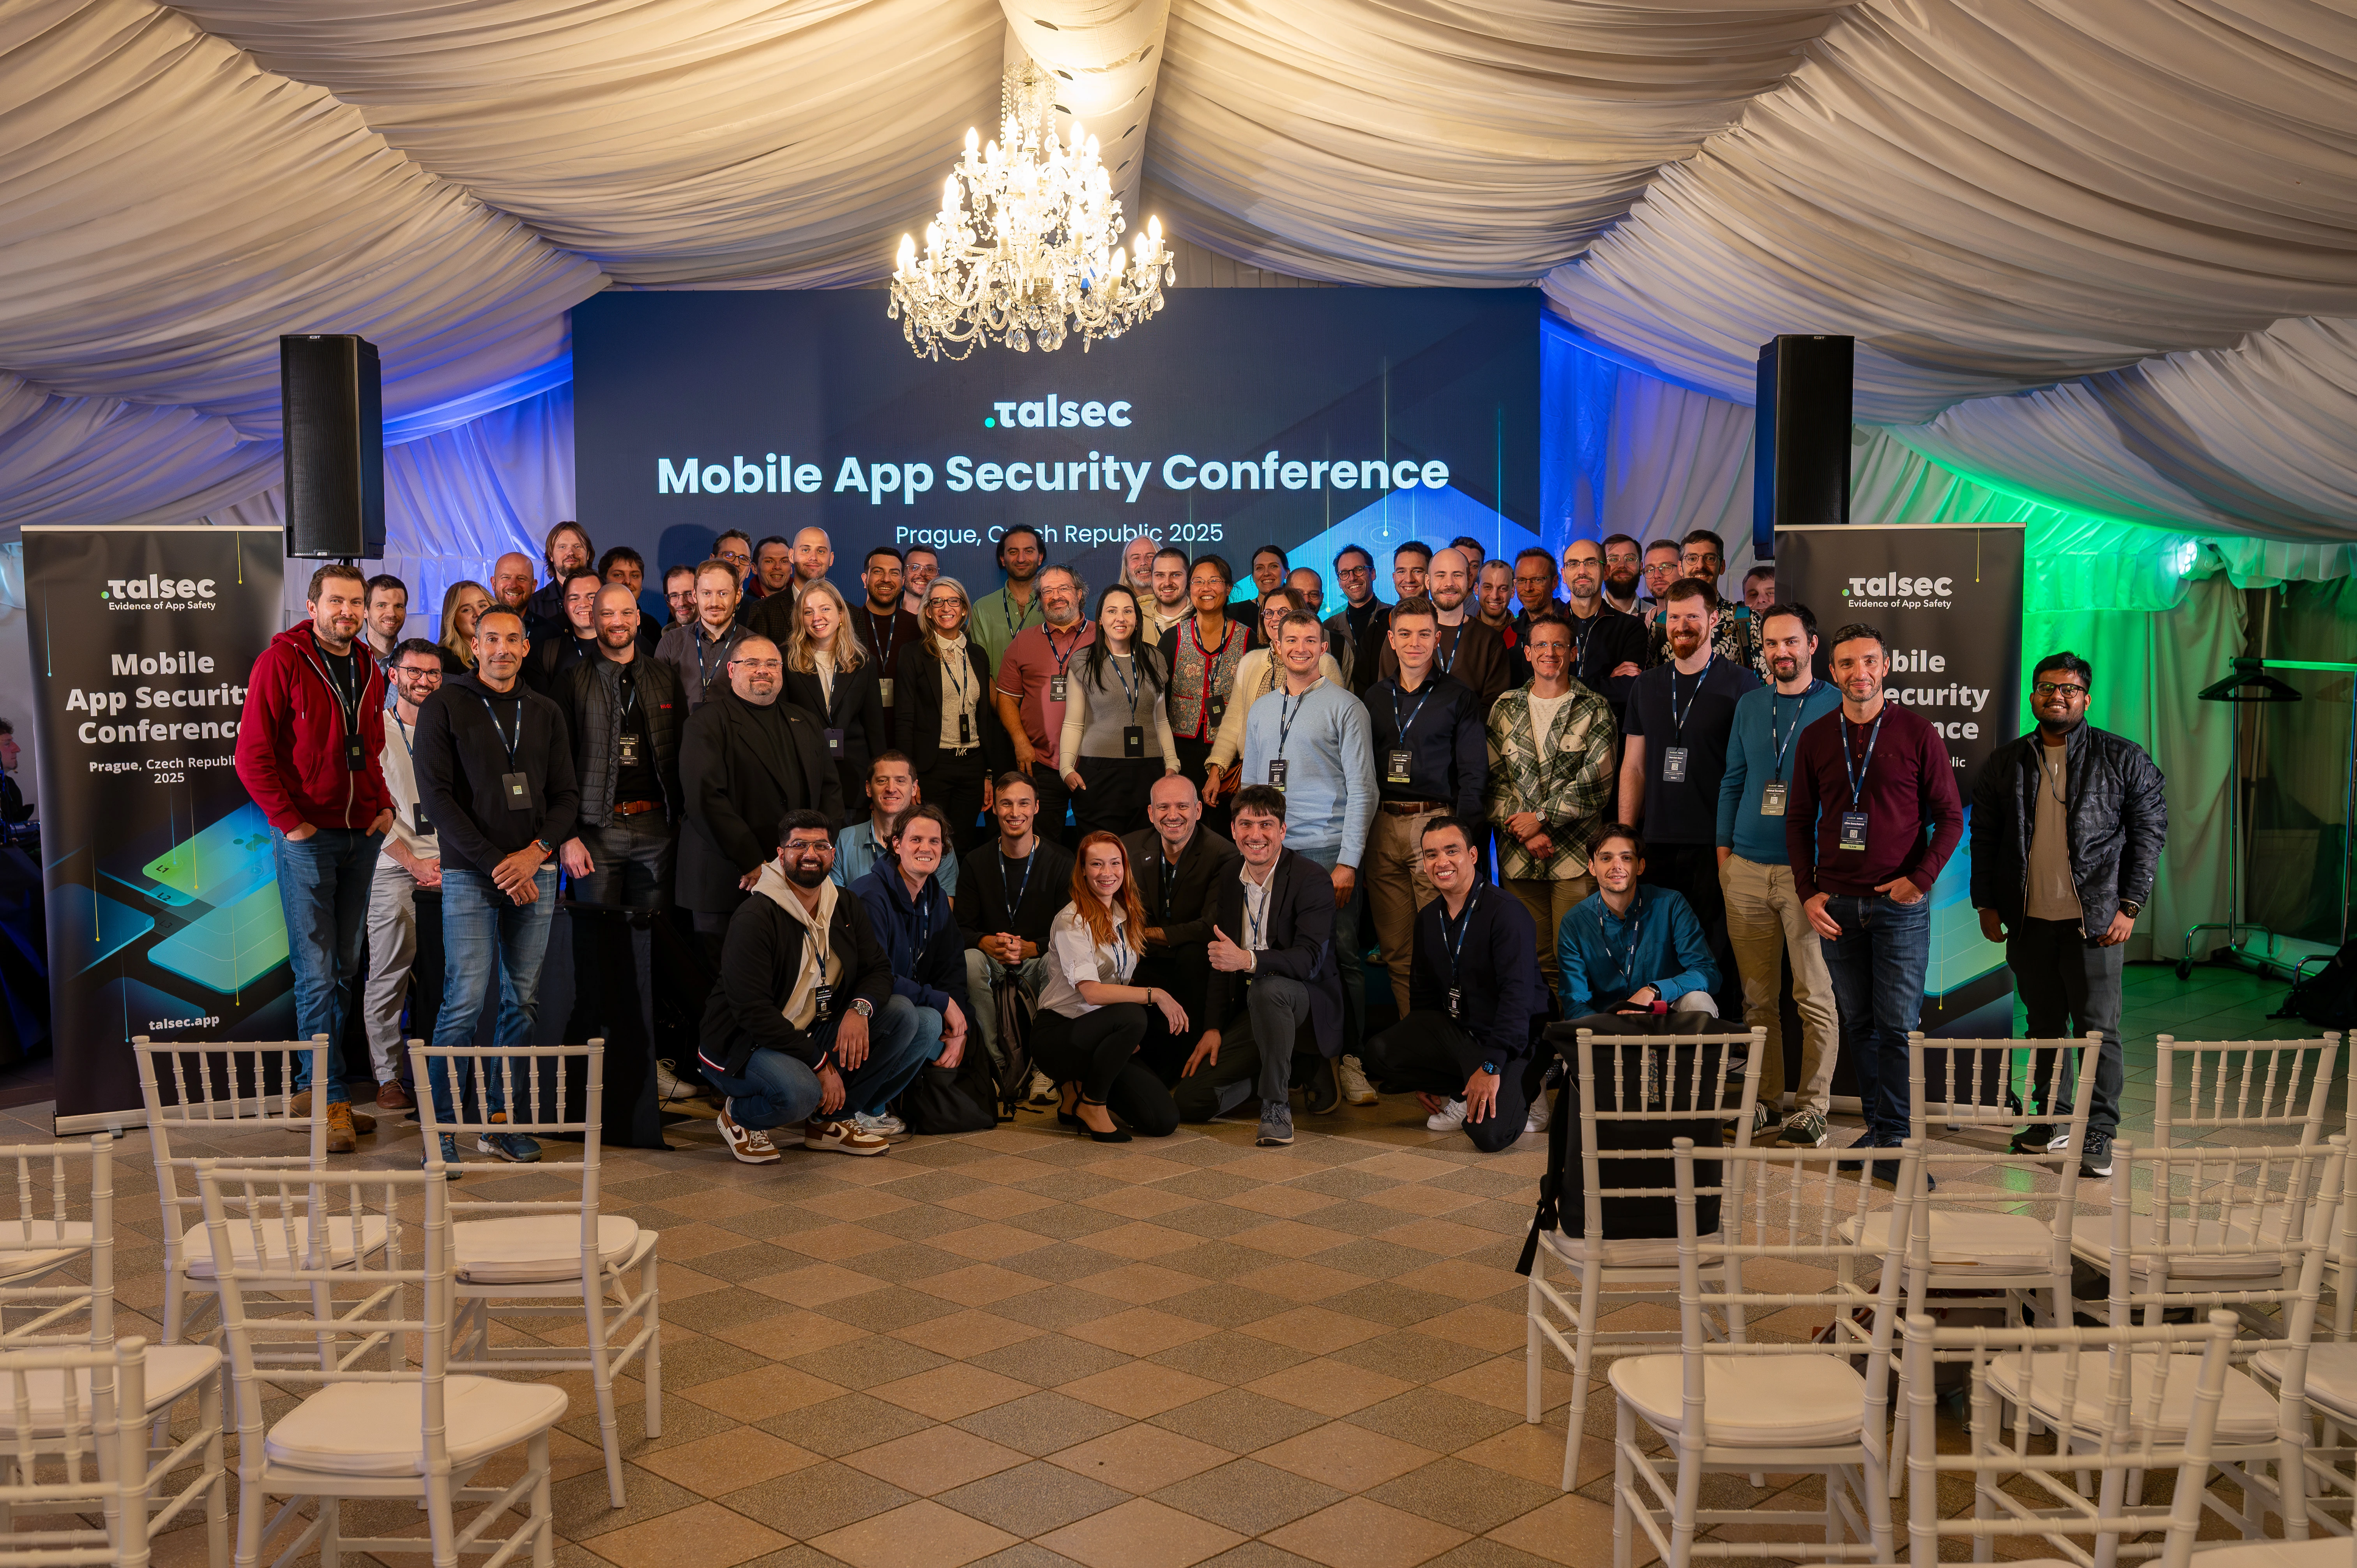
The Haxoris team took the stage at Talsec AppSec Conf in Prague: Red Teaming on stage and a hands-on Android app hacking workshop.
We present the story of our mission, which revealed how scammers in Slovakia and Europe use psychology, social engineering, and technology to defraud people.
Discover what penetration testing is, why it's essential for your cybersecurity, and how Haxoris helps protect your systems from attacks. A complete guide for laymen, cybersecurity managers, and CISOs, including insights on the new Slovak Cyber Law (NIS2).
Is your AI chatbot truly secure? Attacks like prompt injection can reveal sensitive data and manipulate its behavior. Read how to protect LLM applications. Attackers often only need a single, cleverly formulated sentence to break through protective barriers and force the model to ignore its original rules. We offer practical recommendations and insights into specialized tests that reveal weaknesses before someone else can exploit them.
Learn how Haxoris Red Teaming revealed real vulnerabilities through simulated attacks. A practical case study on improving security resilience.
A penetration test is the key that transforms a formal cybersecurity audit into real assurance. Discover why auditors rely on trusted results from Haxoris and how we help you identify and fix weaknesses before they turn into costly incidents.
My research explored how AI-powered LLMs can assist in vulnerability detection and security log analysis. While AI improves efficiency, it also introduces challenges like false positives and cost concerns. The key takeaway is that AI should enhance, not replace, human expertise in cybersecurity.
Explore OWASP methodologies and web security vulnerabilities in PHP applications, presented at Slovak Technical University by Andrej Šebeň.
Ethical hacking can also be fun! Witty and engaging discussions about CVEs, banking security, and real-world cybersecurity stories in the Buzzworld podcast.
Discover how ethical hackers legally test systems and stop cyber threats. Listen to Haxoris’ podcast on ethical hacking, security, and responsible hacking.